Updated Oct 31, 2026
Linux
GetPublicIP Client
The Linux client is in beta. It's ready to use, and new versions arrive with your normal system updates. If something doesn't work, contact us and tell us what happened.
The getpublicip client sets up your public IP from your API key and keeps it working. It:
- installs WireGuard and checks that it works
- connects, and reconnects if the connection stops working
- adds and removes port mappings
- opens the mapped ports in your firewall (ufw, firewalld or iptables)
- warns you when a service can't be reached, for example because it only listens on
127.0.0.1
It supports Ubuntu 26.04 and Debian 13. To install it, follow Debian - GetPublicIP below. On other distributions, set up WireGuard yourself instead.
The client's screens
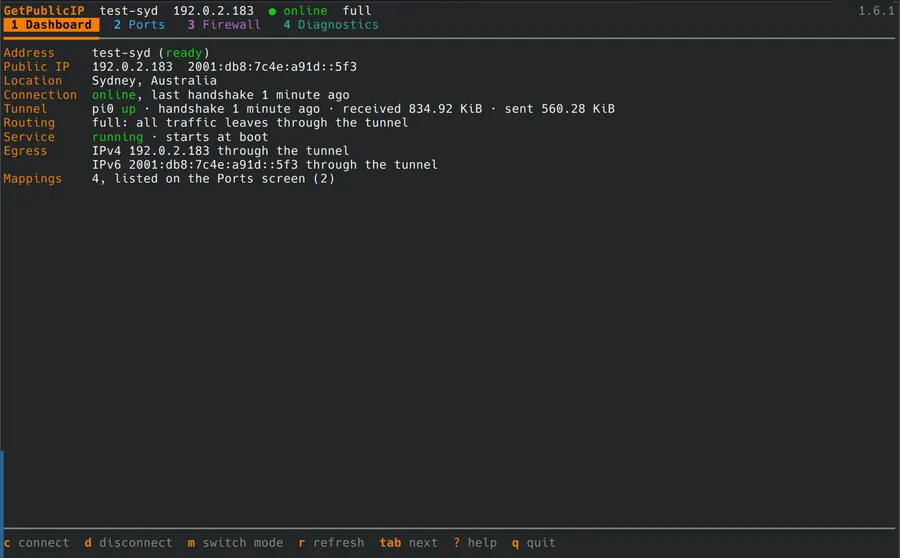
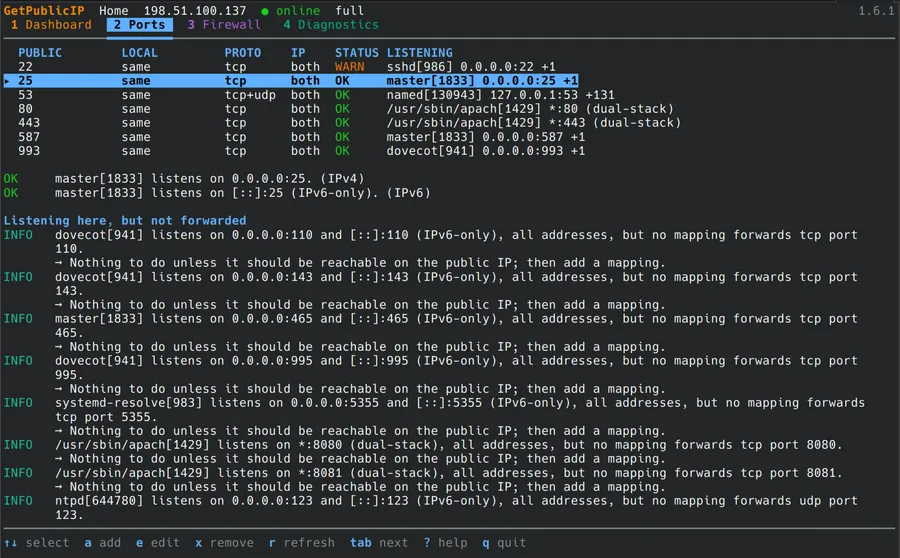
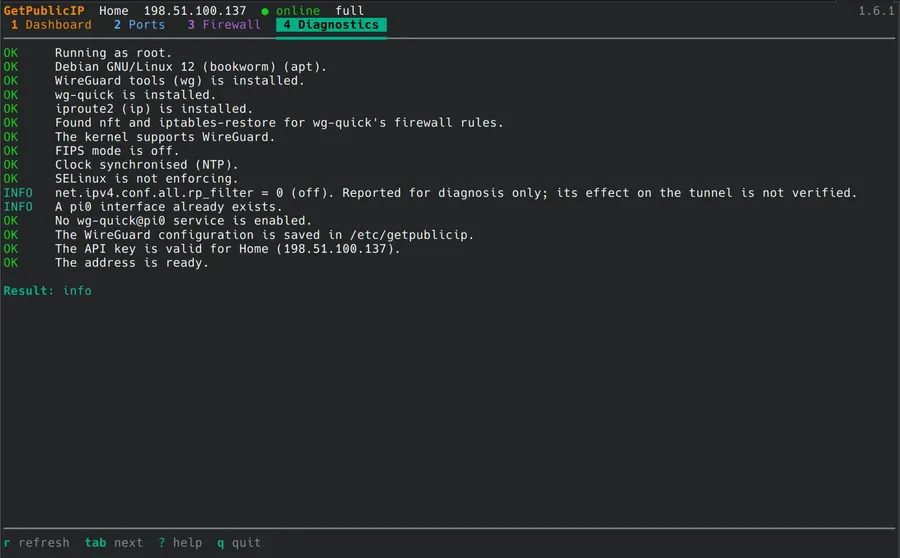
Run sudo getpublicip to open the client in your terminal. The first time, it opens on the setup screen. Once you're set up, it opens on the Dashboard, one of four screens:
- Dashboard: your public IP, the connection, and which IP your traffic uses. Press c to connect, d to disconnect, or m to switch between split and full mode.
- Ports: each forwarded port and whether the service behind it can be reached. Select a port with ↑ ↓, then press a to add, e to edit or x to remove one.
- Firewall: whether your firewall lets the mapped ports in. Press a to open them, or x to remove the rules the client added.
- Diagnostics: whether this machine can run the client, and what to fix if it can't. If a package is missing, press i to install it.
Press 1 to 4 or Tab to switch screens, ? for help, and q to quit.
From the command line
Everything you can do on the client's screens is also a command, so you can skip the screens or use the commands in scripts.
Forward ports
sudo getpublicip ports add 443/tcp # public 443 → local 443
sudo getpublicip ports add 80/tcp --to 8080 # public 80 → local 8080
sudo getpublicip ports add 60000-60099/udp # public 60000-60099 → local 60000-60099
sudo getpublicip ports edit 80/tcp --to 8081 # change the local port to 8081
sudo getpublicip ports rm 80/tcp # stop forwarding port 80
sudo getpublicip ports # list your ports and check each service can be reached
Each service must listen on 0.0.0.0 (or ::), not 127.0.0.1, or connections from the internet can't reach it. sudo getpublicip ports warns you if a service can't be reached.
You can also manage ports in the dashboard. While the getpublicip service is running, the client picks up your changes within about a minute.
Check and troubleshoot
sudo getpublicip status # show your public IP, the connection, and which IP your traffic uses
sudo getpublicip doctor # check this machine and tell you what to fix
Debian - GetPublicIP
These steps install the client on Debian 13 and Ubuntu 26.04.
Install
Add the GetPublicIP repository and install the client:
sudo apt update && sudo apt install -y curl
sudo curl -fsSLo /usr/share/keyrings/getpublicip-archive-keyring.gpg \
https://repo.getpublicip.com/apt/getpublicip-archive-keyring.gpg
sudo curl -fsSLo /etc/apt/sources.list.d/getpublicip.sources \
https://repo.getpublicip.com/getpublicip.sources
sudo apt update && sudo apt install getpublicip
The packages are signed with the GetPublicIP key 99063C03D7A61416F04286C856057FC6E630114F. To check that the key you downloaded matches, run:
gpg --show-keys /usr/share/keyrings/getpublicip-archive-keyring.gpg
A minimal Debian install doesn't include gpg. Install it first with sudo apt install gnupg.
Set up
- Create an API key for your IP address.
- Start the client:
sudo getpublicip - On the setup screen, paste your API key. It stays hidden as you type. Move between fields with Tab or ↑ ↓, and choose an option with ← →.
- Under Mode, choose how this machine uses your public IP:
- Split (recommended for servers): connections to your public IP reach this machine. Everything else, including SSH, uses your normal internet connection.
- Full: all of this machine's internet traffic goes out through your public IP. If you're setting up over SSH, your session stays connected.
- Under At boot, leave start selected so the connection comes back after a reboot and picks up port changes you make in the dashboard. Then press Enter.
Setup checks your system and connects. If it needs to ask you anything, such as whether to use the IP address it found, it asks on screen.
To answer the same questions in the terminal instead, run sudo getpublicip setup.
Debian - WireGuard
If you'd rather manage WireGuard yourself, or your distribution isn't supported by the client, follow these steps. They work on Debian 12 and 13. You'll need to open ports in your firewall yourself.
If you turn off Route all traffic when you download the configuration, bind UDP services to the tunnel address instead of all addresses. Otherwise their replies go out through your normal connection and never reach the sender.
- As root, install WireGuard:
apt install wireguard resolvconf - In the dashboard, download the Linux configuration for your IP address. Copy
pi0.confto/etc/wireguard/:cp pi0.conf /etc/wireguard/ - Start WireGuard:
systemctl start wg-quick@pi0 - To start it at boot:
systemctl enable wg-quick@pi0 - Check that the WireGuard interface is up:
wg show - You're connected. Open the ports you need in your firewall. For example, to open port 80 with ufw:
ufw allow 80/tcp - (Recommended) Install the WireGuard watchdog script. It restarts the connection when it stops working, for example after your ISP gives you a new IP address.
Red Hat - WireGuard
These steps set up WireGuard on Red Hat Enterprise Linux 10. As on Debian, you open ports in your firewall yourself, and if you turn off Route all traffic when you download the configuration, bind UDP services to the tunnel address instead of all addresses.
- As root, install WireGuard:
dnf install wireguard-tools - In the dashboard, download the Linux configuration for your IP address. Copy
pi0.confto/etc/wireguard/:cp pi0.conf /etc/wireguard/ - Start WireGuard:
systemctl start wg-quick@pi0 - To start it at boot:
systemctl enable wg-quick@pi0 - Check that the WireGuard interface is up:
wg show - You're connected. Open the ports you need in your firewall. For example, to open port 80 with firewalld:
firewall-cmd --permanent --zone=public --add-port=80/tcp firewall-cmd --reload - (Recommended) Install the WireGuard watchdog script. It restarts the connection when it stops working, for example after your ISP gives you a new IP address.